Findings and exposure policy
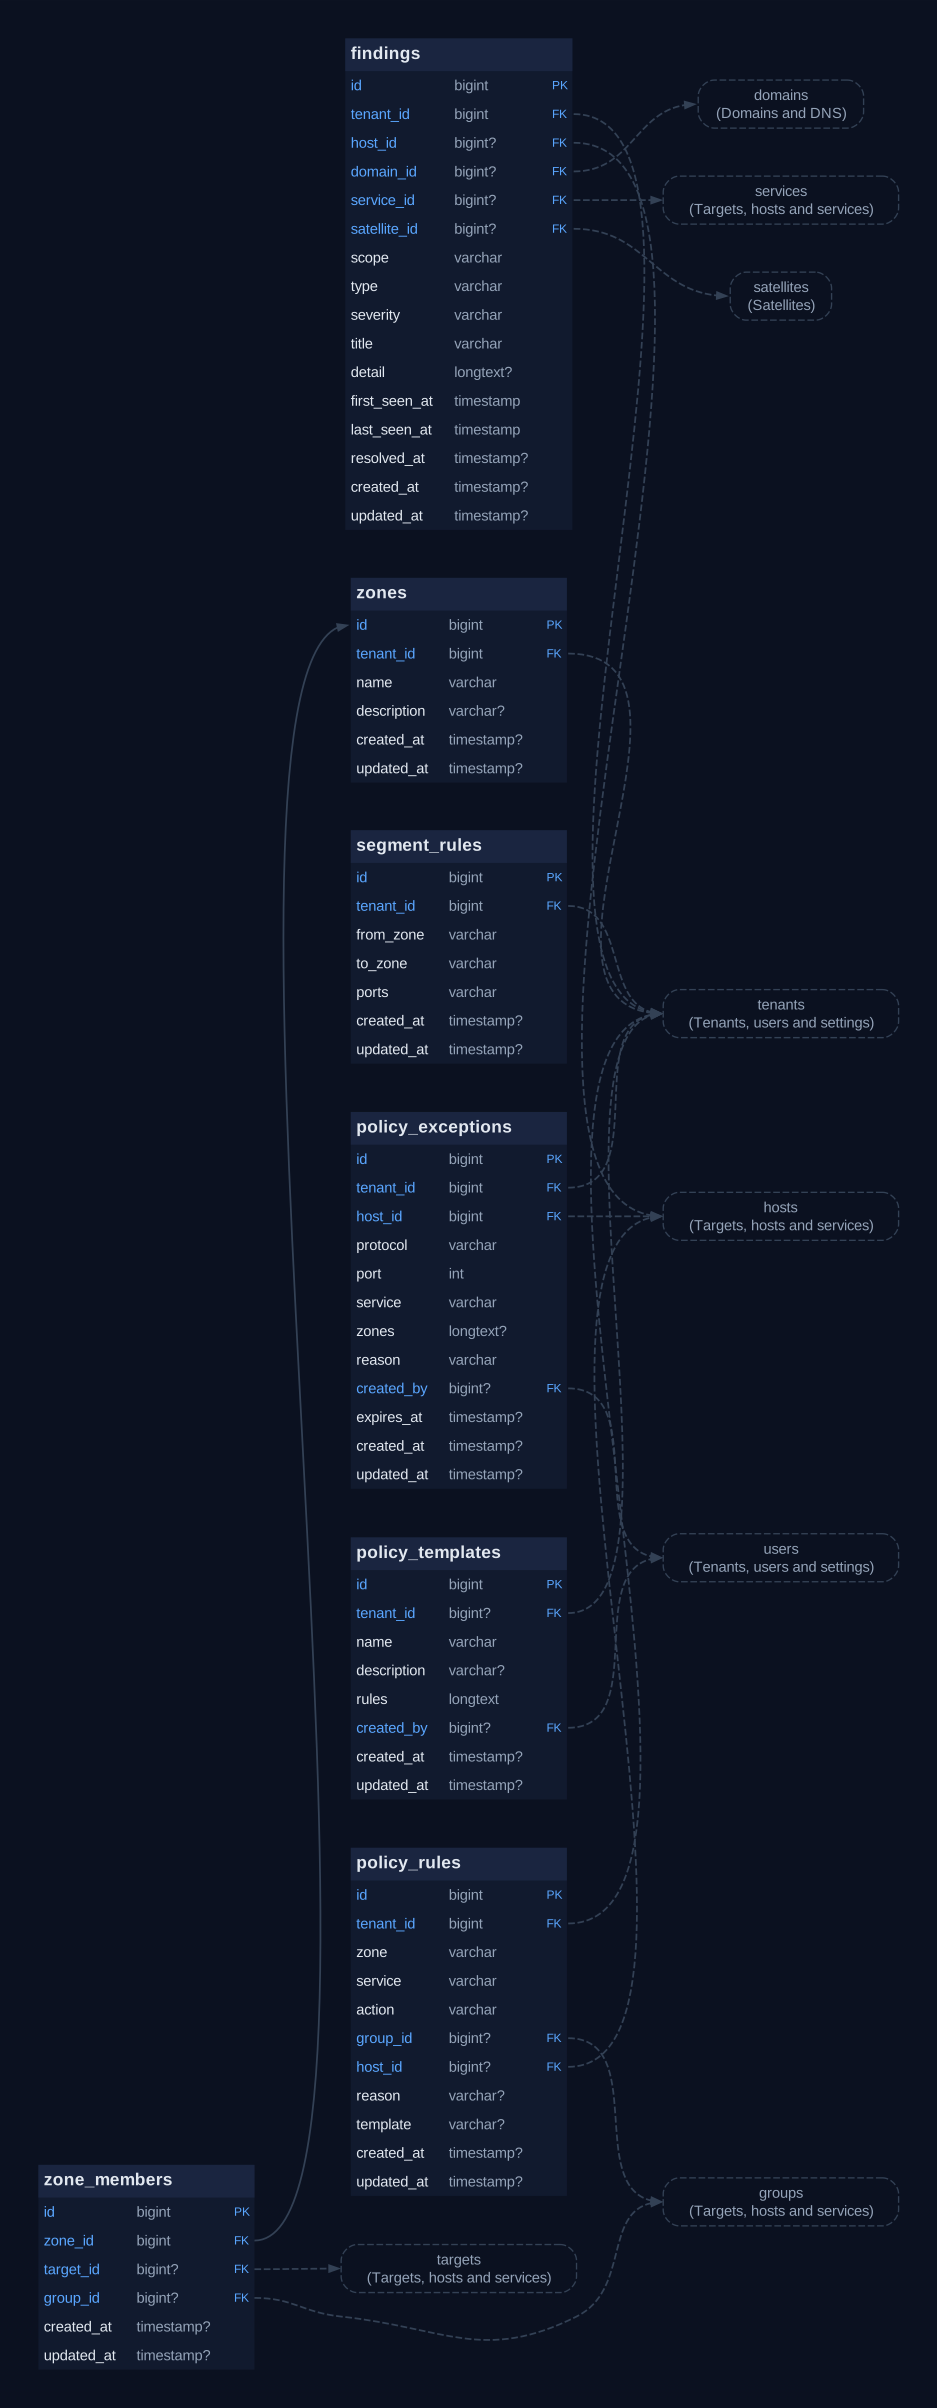
findings
Problems the analyzers found (certificate, TLS, DNS, mail, policy): severity, scope, title, details. Open while the cause is seen, resolved automatically when it is gone.
16 columns
| Column | Type | Null | Default | References |
|---|---|---|---|---|
id PK | bigint(20) unsigned | |||
tenant_id | bigint(20) unsigned | tenants on delete cascade | ||
host_id | bigint(20) unsigned | yes | hosts on delete cascade | |
domain_id | bigint(20) unsigned | yes | domains on delete cascade | |
service_id | bigint(20) unsigned | yes | services on delete set null | |
satellite_id | bigint(20) unsigned | yes | satellites on delete set null | |
scope | varchar(255) | |||
type | varchar(64) | |||
severity | varchar(10) | |||
title | varchar(255) | |||
detail | longtext | yes | ||
first_seen_at | timestamp | |||
last_seen_at | timestamp | |||
resolved_at | timestamp | yes | ||
created_at | timestamp | yes | ||
updated_at | timestamp | yes |
Indexes: domain_id · host_id · satellite_id · service_id · tenant_id, resolved_at, severity · tenant_id, scope, type (unique)
zones
Network zones of a tenant (e.g. office, dmz). A satellite sits in a zone through its manual zone tag; external is reserved.
6 columns
| Column | Type | Null | Default | References |
|---|---|---|---|---|
id PK | bigint(20) unsigned | |||
tenant_id | bigint(20) unsigned | tenants on delete cascade | ||
name | varchar(60) | |||
description | varchar(255) | yes | ||
created_at | timestamp | yes | ||
updated_at | timestamp | yes |
Indexes: tenant_id, name (unique)
zone_members
Targets or groups that belong to a zone, used by the segmentation matrix.
6 columns
| Column | Type | Null | Default | References |
|---|---|---|---|---|
id PK | bigint(20) unsigned | |||
zone_id | bigint(20) unsigned | zones on delete cascade | ||
target_id | bigint(20) unsigned | yes | targets on delete cascade | |
group_id | bigint(20) unsigned | yes | groups on delete cascade | |
created_at | timestamp | yes | ||
updated_at | timestamp | yes |
Indexes: group_id · target_id · zone_id
policy_rules
Exposure policy: a service is allowed or forbidden in a zone (or all zones), for the tenant, a group or a host.
11 columns
| Column | Type | Null | Default | References |
|---|---|---|---|---|
id PK | bigint(20) unsigned | |||
tenant_id | bigint(20) unsigned | tenants on delete cascade | ||
zone | varchar(60) | * | ||
service | varchar(32) | |||
action | varchar(8) | |||
group_id | bigint(20) unsigned | yes | groups on delete cascade | |
host_id | bigint(20) unsigned | yes | hosts on delete cascade | |
reason | varchar(255) | yes | ||
template | varchar(60) | yes | ||
created_at | timestamp | yes | ||
updated_at | timestamp | yes |
Indexes: group_id · host_id · tenant_id, service
policy_exceptions
Accepted deviations: one port and service on one host, optionally per zone and until a date, with the reason.
12 columns
| Column | Type | Null | Default | References |
|---|---|---|---|---|
id PK | bigint(20) unsigned | |||
tenant_id | bigint(20) unsigned | tenants on delete cascade | ||
host_id | bigint(20) unsigned | hosts on delete cascade | ||
protocol | varchar(8) | tcp | ||
port | int(10) unsigned | |||
service | varchar(32) | |||
zones | longtext | yes | ||
reason | varchar(500) | |||
created_by | bigint(20) unsigned | yes | users on delete set null | |
expires_at | timestamp | yes | ||
created_at | timestamp | yes | ||
updated_at | timestamp | yes |
Indexes: created_by · host_id, port · tenant_id
policy_templates
Rule sets saved by a tenant as templates.
8 columns
| Column | Type | Null | Default | References |
|---|---|---|---|---|
id PK | bigint(20) unsigned | |||
tenant_id | bigint(20) unsigned | yes | tenants on delete cascade | |
name | varchar(120) | |||
description | varchar(500) | yes | ||
rules | longtext | |||
created_by | bigint(20) unsigned | yes | users on delete set null | |
created_at | timestamp | yes | ||
updated_at | timestamp | yes |
Indexes: created_by · tenant_id
segment_rules
Segmentation matrix: ports allowed from one zone to another.
7 columns
| Column | Type | Null | Default | References |
|---|---|---|---|---|
id PK | bigint(20) unsigned | |||
tenant_id | bigint(20) unsigned | tenants on delete cascade | ||
from_zone | varchar(60) | |||
to_zone | varchar(60) | |||
ports | varchar(500) | |||
created_at | timestamp | yes | ||
updated_at | timestamp | yes |
Indexes: tenant_id, from_zone, to_zone (unique)