Tenants, users and roles
Multi-tenancy, the five roles, products per tenant, sign-in with password, TOTP or OIDC.
Roles
| Role | Scope | Can |
|---|---|---|
| Viewer | tenant | see everything of the tenant |
| Editor | tenant | add and edit targets, hosts, groups, plans, domains; run checks; set host locations |
| Admin | tenant | additionally: products (Features), notification channels, reports, exposure policy, tenant satellites, members |
| Operator | global | admin in every tenant; edits every tenant’s parameters; creates satellites for any tenant or globally |
| Super admin | global | additionally users and System settings |
A user has one role per tenant and switches between tenants in the top bar. The two global roles are flags on the user (or come from OIDC groups).
Products per tenant
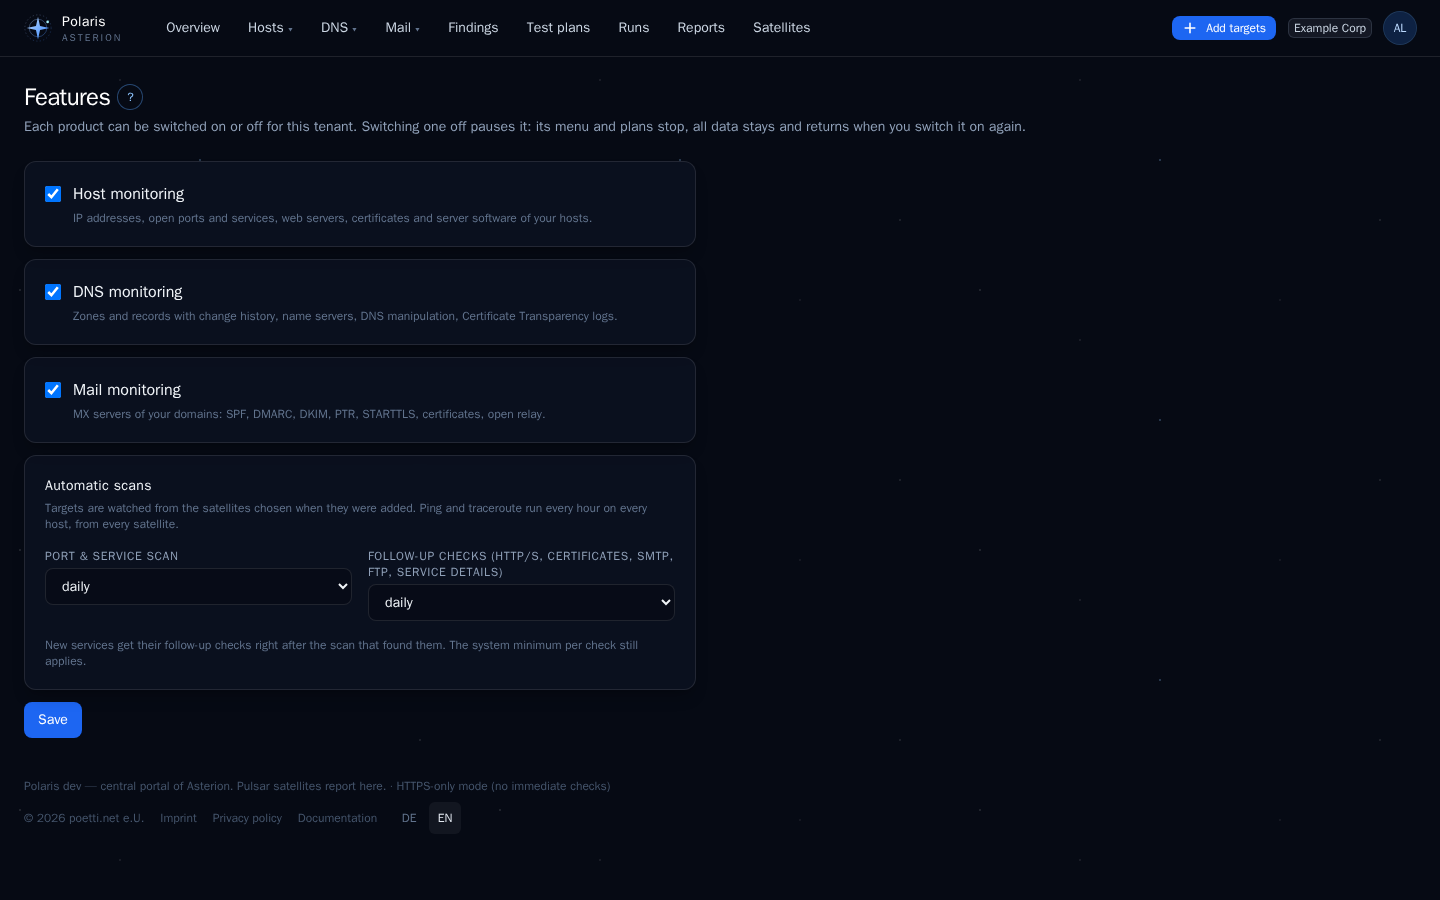
Features (tenant admins, operators): switch Host, DNS and Mail monitoring on or off, and set the intervals of the automatic port scan and its follow-up checks (hourly, every 6 or 12 hours, daily, weekly; default daily).
Sign-in
- Password with optional TOTP (authenticator app) and recovery codes. Super admins can require TOTP for all local users.
- OIDC (Microsoft Entra ID, Keycloak, any compliant provider) with PKCE. Users are created on first login (
OIDC_AUTO_CREATE_USERS) inOIDC_DEFAULT_TENANTwithOIDC_DEFAULT_ROLE. Members ofOIDC_ADMIN_GROUPbecome super admins, ofOIDC_OPERATOR_GROUPoperators.OIDC_DISABLE_LOCAL_LOGINhides the password form. - Login, TOTP and password reset are rate limited.
My account
Users change their name, language, password and TOTP, and download their data as JSON (GDPR Art. 15/20). Accounts are deleted by an administrator.