Notifications and reports
Who is told what, when — and the recurring change reports for audits.
Notification channels
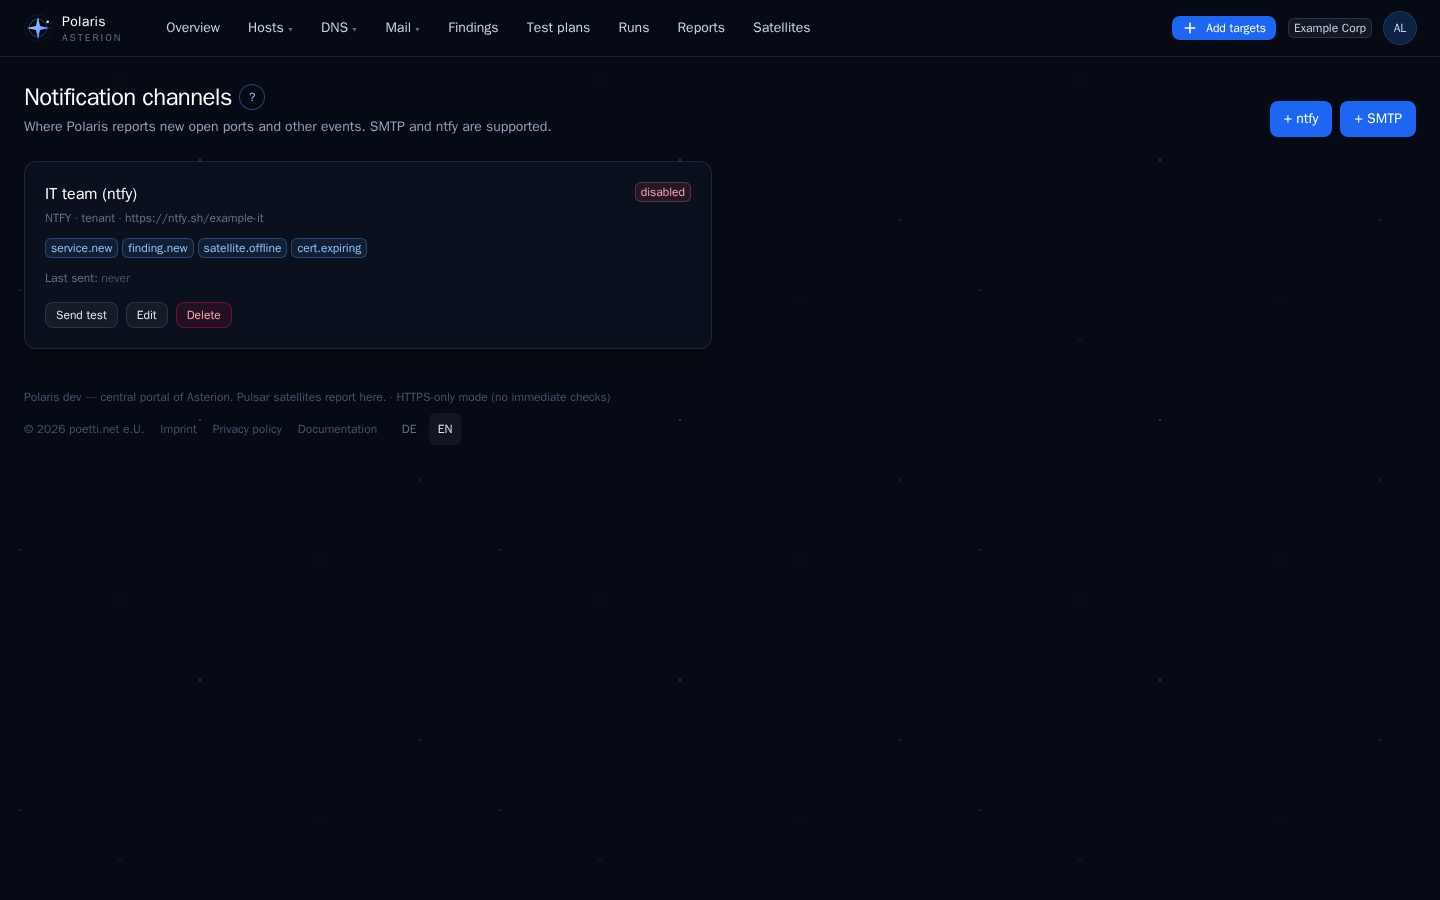
Tenant admins add channels under Notifications:
- SMTP — through the tenant’s own mail server, or the system mail server (System settings, else
MAIL_*) when none is set. - ntfy — ntfy.sh or a self-hosted ntfy server, with optional access token.
Servers in internal networks are refused unless a super admin allowed them (Internal notification servers).
Each channel subscribes to events. Credentials are stored encrypted with APP_KEY. Test sends a test message. Global channels (no tenant) receive the events of every tenant.
Events
| Event | Meaning |
|---|---|
service.new | New open service |
service.gone | Service disappeared |
service.changed | Service fingerprint changed |
host.down | Host unreachable |
cert.expiring | Certificate expiring / invalid |
satellite.offline | Satellite offline |
run.failed | Scan run failed / overdue |
finding.new | New finding (warning / critical) |
policy.violation | Exposure policy violation |
cert.changed | Certificate changed on an endpoint |
dns.changed | DNS records / name servers changed |
dns.mail_changed | Mail DNS records changed (MX, SPF, DMARC, DKIM, MTA-STS) |
rir.changed | Registry / routing data changed (RIR, prefix, origin AS) |
ct.new | New certificate in Certificate Transparency logs |
- The first result is a baseline and never notifies: a new host’s services, a new domain’s records, the first CT poll.
finding.newis sent for new findings of severity warning and critical, not for info.satellite.offlineand an overdue plan (run.failed) are sent once until the state recovers.
Reports
Recurring reports per product, for ISMS and audit evidence: daily (yesterday), weekly (last seven days), monthly (previous month) or yearly (previous year), in the report’s timezone. Each lists every change of its product with the moment it was noticed and the satellite that saw it: services, certificates, software versions, registry data, DNS records, CT logs, mail records, findings opened and resolved.
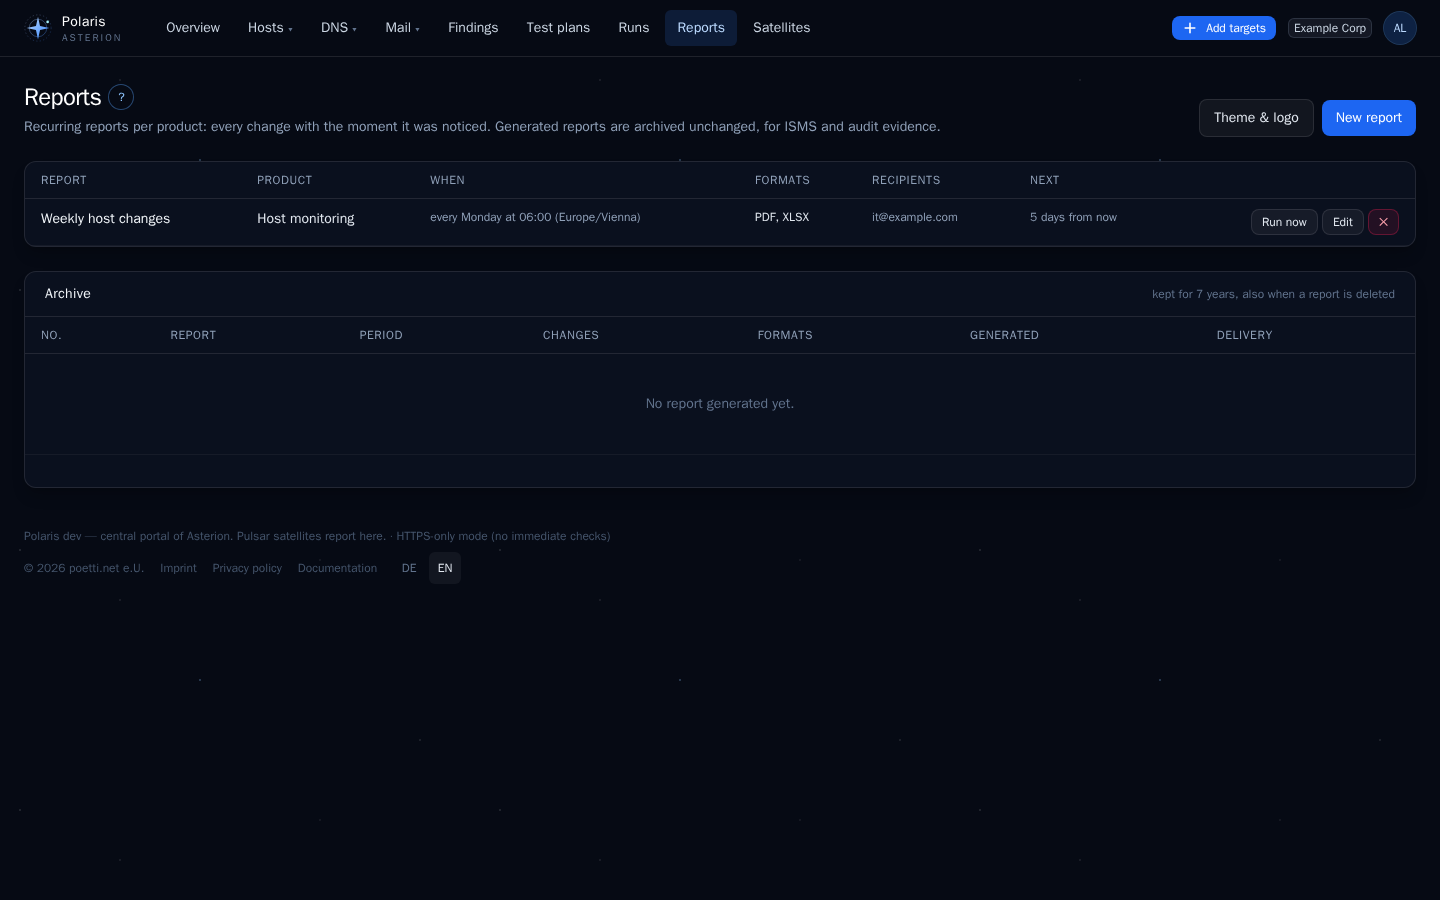
- Formats: PDF, CSV, Excel and OpenDocument. A PDF shows up to 1000 changes per section and says so when it stops; the spreadsheets hold all. Values from scanned systems are written as text, so they cannot become spreadsheet formulas.
- Sent by e-mail through the tenant’s SMTP channel if it has its own server, else the system mail server.
- Company name, colour, footer and logo (PNG/JPEG) are set once per tenant (Report theme).
Archive and integrity
Every generated report is stored unchanged for POLARIS_RETENTION_REPORTS_YEARS (7), also when its definition is deleted. Each file has a SHA-256, and each report a hash over its files, its period and the previous report of the tenant. The archive verifies the chain on every view: a changed, removed or inserted report shows up as a failed integrity check.
Note
This makes changes evident; it does not prevent them. Someone with write access to the database could recompute the whole chain. Keep the checksums from the e-mails outside Polaris if that matters to you.